Dangerous Ads: Billions of Impressions, Spyware, and a Threat to Crypto Wallets
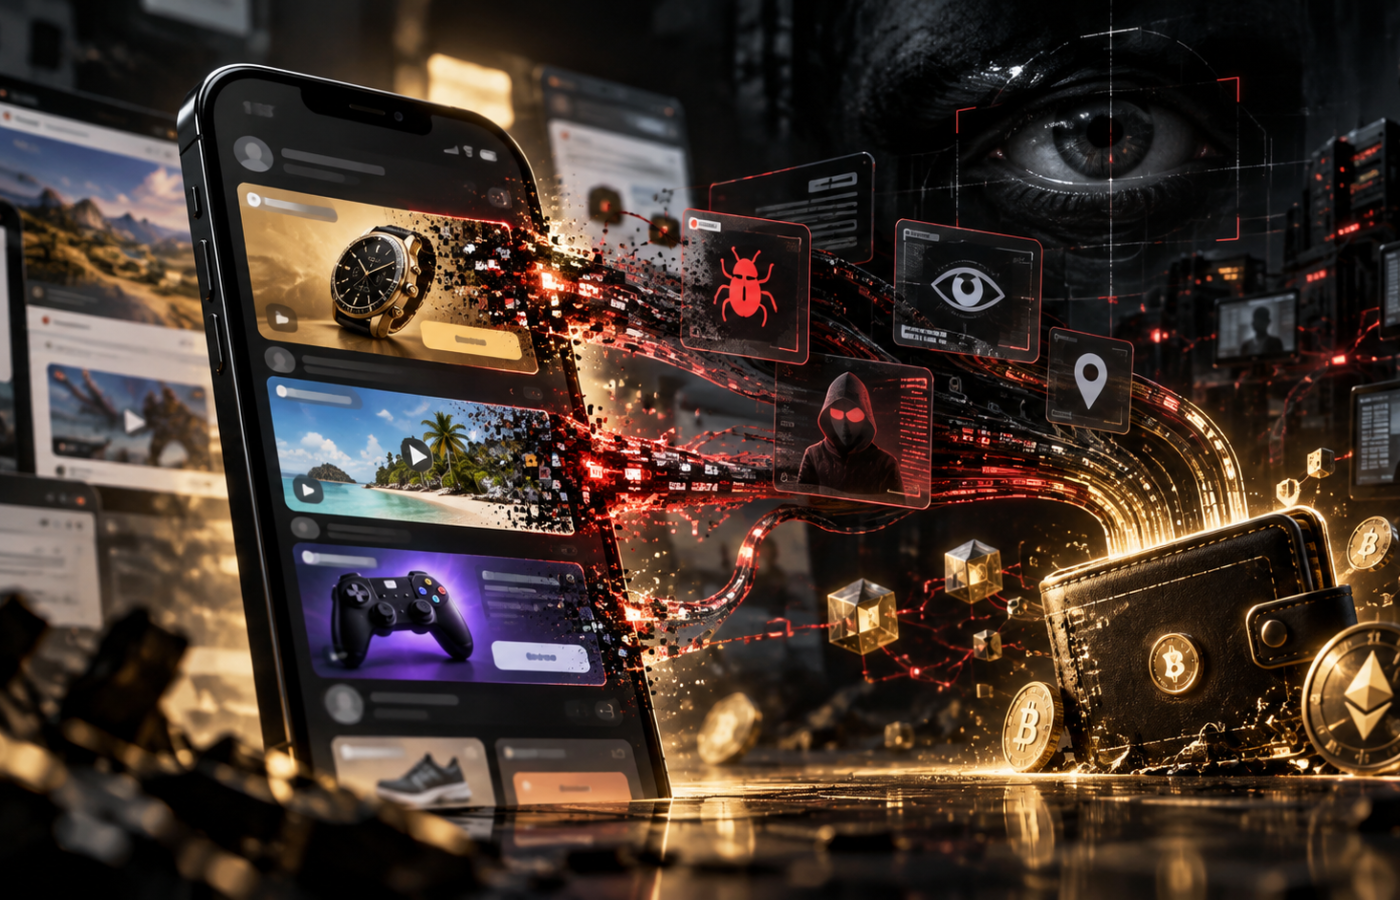
Dangerous ads have become a weapon of digital espionage. Nearly 4 billion advertising auction records, around 200,000 websites and applications, millions of devices exposed to surveillance, and confirmed infections involving professional spyware. And the most disturbing part? Victims didn’t even need to click on an advertisement. An investigation published on October 15 uncovered a massive surveillance system operating inside the advertising infrastructure of the modern internet. Now consider how many ads people voluntarily watch every day on websites, in mobile games, and on Telegram in exchange for free rewards. How secure are their personal data and cryptocurrency wallets?
Four Billion Advertising Records. And That’s Just the Beginning
On October 15, researchers from Citizen Lab and Confiant exposed the activities of Discover-Tech, a company that used advertising infrastructure for surveillance and spyware delivery.
The scale was staggering:
- Nearly 4 billion advertising auction records collected over four months.
- More than 120,000 websites and 70,000 mobile applications.
- Millions of devices communicating with infrastructure associated with tracking and potential infection.
- Confirmed attacks involving the professional Candiru spyware.
- Advertising infrastructure operated by Google, Yandex, Beeswax, and other major providers.
But the most interesting detail was something else entirely.
Discover-Tech had been listed in advertising industry registries, including those associated with Google and IAB Europe, since 2020.
In other words, the company had access to legitimate advertising infrastructure for years while maintaining a system that researchers linked to professional digital espionage.
Following the investigation, Google terminated Discover-Tech’s access to its advertising platforms. Other advertising operators also blocked or restricted the company’s activities.
Hacking Without a Single Click
The uncovered operation was named AdFection.
Its advertising infrastructure collected technical device identifiers, matched them against selected targets, and determined which users should receive additional code.
An ordinary user might see a completely normal advertisement or not even notice it.
But when a device matched the attackers’ targeting criteria, the system could deliver malicious JavaScript designed to initiate an infection chain.
No suspicious links. No file downloads. No installation confirmations.
The malicious code exploited software vulnerabilities to break out of the normal restrictions imposed on advertising content.
Researchers confirmed the use of Candiru spyware in attacks targeting devices belonging to the international media organization Al Jazeera. At least 45 devices were targeted during the campaign, although successful infection was not independently confirmed for every device.
This was no longer a theoretical discussion about potentially dangerous advertising.
It was a documented mechanism used in real-world spyware attacks.
Even Ordinary Advertising Can Reveal Too Much
Surveillance does not necessarily require compromising a device.
Advertising networks can collect IP addresses, device identifiers, browser information, operating system details, and data about user activity.
Combining this information makes it possible to link a person’s activities across different websites and applications.
Discover-Tech used similar mechanisms to correlate identifiers and track selected devices.
And that raises an uncomfortable question.
If an advertising company can identify where a particular device appears, which applications it uses, and which servers it communicates with, how anonymous is that user?
Especially when the same device is used for social media, Telegram, and cryptocurrency transactions.
Telegram: Security Issues Found in 30 of 37 Applications
Now let’s turn our attention to Telegram.
In August 2026, researchers published TENET, a study examining the security of Telegram Mini Apps.
Of the 61 applications initially selected, 37 underwent a complete analysis.
Security weaknesses were discovered in 30 of them. That’s more than 81% of the analyzed sample.
The findings included:
- Sensitive information stored in plaintext.
- Inadequate protection of authentication tokens.
- Encrypted secrets that could potentially be recovered.
- Insecure storage of cryptocurrency wallet information.
A serious vulnerability was even identified in the official Telegram Wallet. It could potentially have led to wallet compromise. After being notified, the developers addressed the issue involving plaintext storage of the recovery phrase.
It is important to emphasize that the study covered a limited sample, not the entire Telegram ecosystem.
But there was another investigation.
In a separate study called TeleGapper, researchers analyzed 278 Telegram Mini Apps.
The results were equally concerning.
59.4% of the applications communicated with at least one third party not disclosed in their privacy policies.
Meanwhile, 78.8% relied exclusively on Telegram’s standard privacy policy.
In other words, users do not always know which external services receive information from the applications they use.
Against this background, the enormous industry built around watching advertisements in exchange for gaming coins, energy, and other virtual rewards becomes particularly interesting.
What Happens If These Two Technologies Are Combined?
This is where the scenarios become genuinely disturbing.
Scenario One: Invisible Surveillance
A user regularly watches advertisements in mobile games, on websites, and inside Telegram Mini Apps.
Different advertising systems collect information about the device. When shared identifiers are available, activity across multiple platforms can potentially be linked.
Advertising history can therefore become a valuable source of information about a person’s habits and interests.
Professional spyware is not required for this kind of tracking.
Scenario Two: Infection Through an Advertisement
An attacker gains the ability to distribute malicious code through an advertising intermediary.
On a vulnerable device, that code could potentially reproduce an attack similar to AdFection by exploiting security flaws in a browser, WebView, or operating system.
Technically, this type of attack is also possible in applications that use embedded browsers.
However, researchers have not presented confirmed evidence of AdFection being deployed through Telegram.
Scenario Three: Cryptocurrency Wallets Become Targets
A user launches an application, connects a cryptocurrency wallet, and interacts with advertising content.
If malicious code exploits an application vulnerability and gains access to poorly protected secrets, the consequences could include account or wallet compromise.
Another possible attack involves manipulating a transaction confirmation request.
But one distinction is essential: simply viewing an advertisement does not automatically reveal private keys or authorize cryptocurrency transfers.
An attacker would need to overcome additional security protections or deceive the user.
Free Rewards. But Who Is Really Paying Whom?
Today, practically everything is offered as a reward for watching advertisements.
Gaming currency, additional attempts, energy, faster token mining, and other bonuses.
Users voluntarily return to advertising blocks dozens of times.
And this creates a rather interesting economic model.
For a few seconds of attention, a user receives a hypothetical 100 virtual coins.
The advertising infrastructure receives an impression, an opportunity to collect technical data, and a potential interaction with a specific device.
Of course, not every advertising network engages in surveillance or distributes malicious code.
But the Discover-Tech investigation demonstrated that legitimate advertising infrastructure can be used for purposes far beyond ordinary marketing.
Meanwhile, research into Telegram Mini Apps has shown that even popular applications do not always adequately protect confidential information.
So what happens if these two security problems eventually meet inside the same application?
Conclusion
The AdFection investigation demonstrated just how dangerous an ordinary advertisement can become.
Nearly four billion advertising auction records, hundreds of thousands of websites and applications, millions of devices exposed to surveillance infrastructure, and confirmed infections involving professional spyware.
This is no longer a collection of frightening stories about hackers and suspicious links.
It is a real technology discovered within the advertising infrastructure of some of the world’s largest internet companies.
And although there is currently no evidence that the same operation was deployed through Telegram, research into Mini App security provides sufficient reason to question the risks.
Especially when cryptocurrency wallets are involved.
However, the greatest irony of this entire story is not even the possibility of infection without a click.
For years, we were taught not to open suspicious links. Now it turns out that sometimes you don’t have to open anything at all. The advertisement will find you.
And while some users celebrate receiving another hundred free coins, others may be collecting information about them that is worth considerably more.
Sources
- Citizen Lab, October 15, 2026. Exposing AdFection: Full Investigation into Spyware Advertising Infrastructure
- Citizen Lab. Key Findings of the AdFection Investigation
- Reuters, October 15, 2026. Discover-Tech and the Use of Online Advertising for Digital Espionage
- Financial Times, October 15, 2026. Zero-Click Spyware Delivered Through Online Advertising
- TENET: Telegram Mini App (in)security. Research on the Security of 37 Mini Apps
- TeleGapper: On the (un)reliability of Privacy Policies in Telegram Mini Apps. Analysis of 278 Applications